Setting Up
Using GPT-6 Astra? Switching models can require changing the endpoint and request/response handling. Use Astra with Responses for Python, JavaScript, curl, and MCP examples. Astra function tools require Responses, and none is not a supported reasoning effort.
Get Started on DeepIntShield Cloud
Section titled “Get Started on DeepIntShield Cloud”DeepIntShield is a fully hosted cloud gateway. There’s nothing to install - sign up, create a virtual key, and point your SDK or base URL at https://app.deepintshield.com. Connect to any AI provider (OpenAI, Anthropic, Bedrock, and more) through a unified API that follows OpenAI request/response format.
1. Sign Up
Section titled “1. Sign Up”Create your account at https://app.deepintshield.com. The hosted gateway and Web UI require no local server installation; workspace and plan features become available after account provisioning.
2. Create a Virtual Key
Section titled “2. Create a Virtual Key”In the Web UI, add your AI provider API keys and create a virtual key to authenticate your requests. Virtual keys (prefixed sk-ds-) give you a single credential that works across every provider, with built-in governance, rate limiting, and usage tracking.
🖥️ The Web UI provides:
- Visual provider setup - Add API keys with clicks, not code
- Live configuration - Changes require no gateway restart; verify propagation on the next request and across replicas
- Live monitoring - Request logs, metrics, and analytics
- Governance management - Virtual keys, usage budgets, and more
3. Point Your Base URL at the Cloud
Section titled “3. Point Your Base URL at the Cloud”Set your SDK’s provider-specific base_url (or use the Python SDK below).
OpenAI-compatible clients normally use https://app.deepintshield.com/openai;
the unified curl endpoint is https://app.deepintshield.com/v1. Anthropic,
Gemini, Bedrock, and framework compatibility routes use their documented
prefixes. Verify the endpoint and supported feature before migrating production
traffic.
For Python:
pip install "deepintshield[openai]==3.2.0"from deepintshield import DeepintShield
shield = DeepintShield(virtual_key="sk-ds-your-virtual-key")client = shield.openai()See the Python SDK quickstart for every SDK surface.
4. Test Your First API Call
Section titled “4. Test Your First API Call”curl -X POST https://app.deepintshield.com/v1/chat/completions \ -H "Content-Type: application/json" \ -H "x-deepintshield-vk: sk-ds-your-virtual-key" \ -d '{ "model": "openai/gpt-4o-mini", "messages": [{"role": "user", "content": "Hello, DeepIntShield!"}] }'🎉 That’s it! DeepIntShield is routing your AI requests through the hosted cloud gateway.
What You Get
Section titled “What You Get”- Zero-infrastructure start: nothing to install or operate - configure everything through the Web UI
- OpenAI-compatible API: send the same request/response format you already use
- One endpoint for every provider:
/v1/chat/completionsworks with OpenAI, Anthropic, Bedrock, and more - Model selection by name: prefix the model with the provider, e.g.
openai/gpt-4o-mini - Built-in authentication, rate limiting, and routing with no extra wiring
Start a Governed Agent
Section titled “Start a Governed Agent”To run test2.py against a gateway on your own laptop, use the complete
Microsoft Entra + local DeepIntShield walkthrough.
It starts with the Microsoft API, Agent ID blueprint and management application,
then configures http://localhost:8080, encrypted pasted credentials, automatic
Gateway.Invoke assignment and approval of math-agent’s runtime key and code.
For an agent that calls governed tools, continue with the simple-math-agent walkthrough:
- Under Agentic → Identities → Identity providers, configure, enable, and validate its workload token verifier. For a new shared Entra setup, choose Shared agents · explicit identity list; the initially empty list admits nobody and needs no placeholder child ID.
- To create or link an identity from DeepIntShield, open Provisioning → Authorize provisioning and select the verifier. For Entra, select Paste credentials to store its approved management application’s credentials encrypted on the gateway; a credential environment variable or manual encryption-key setup is not required. Other connectors use their server-configured management references. Then Save connection and Check connection. After the check completes in Activity, use Create or link identity and wait for that job to complete. Provisioning saves the expected identity declaration; verification settings are inherited from the provider. Existing externally managed identities can also use the manual declaration flow described in the walkthrough.
- Keep a stable
DEEPINTSHIELD_AGENT_NAME. For Entra gateway runtime authentication, enable the provider’s exchange with its separate blueprint credential, run the SDK with theruntimeextra, and explicitly authorize the reported runtime key before rerunning for proof. Direct-mode workloads instead supply their provider credentials. Run the saved Python file to report identity proof and code. - Open Agentic → Agents → Needs attention → Registrations → Review. Complete Identity & owner, Code & changes, Tools & access, and Runtime access. Select only required actions and resource permissions, inspect Validate changes, then open Review & decide → Preview approval → Confirm approval and access. Rerun the workload and inspect Activity → Runs / Decisions. Reuse the same identity on later runs; creating an identity does not itself approve the agent.
The steps above use local execution. In a workspace with optional server-managed execution enabled, the SDK saves a supported LangGraph submission once and the review drives its server run; see managed execution before retrying.
The workload identity guide covers customer authorization, the four provisioning connectors, and secure credential delivery. Ordinary inference calls above do not require this Agentic registration flow.
Continue with the Agentic Security guide for tool and schema drift, runtime policy, temporary delegation, task controls, action approvals, enrolment, and evidence review. MCP Registry manages live MCP connections and their execution settings. Activity → Audit shows recent access changes, while provisioning jobs remain under Identities → Provisioning → Activity.
Self-Host (Enterprise)
Section titled “Self-Host (Enterprise)”Prefer to run DeepIntShield inside your own VPC or on-premise data plane? The Enterprise / Self-Hosted option lets you deploy the gateway on your own infrastructure while the control plane experience remains the same. See the Deployment Guides to get started.
How DeepIntShield Cloud Is Configured
Section titled “How DeepIntShield Cloud Is Configured”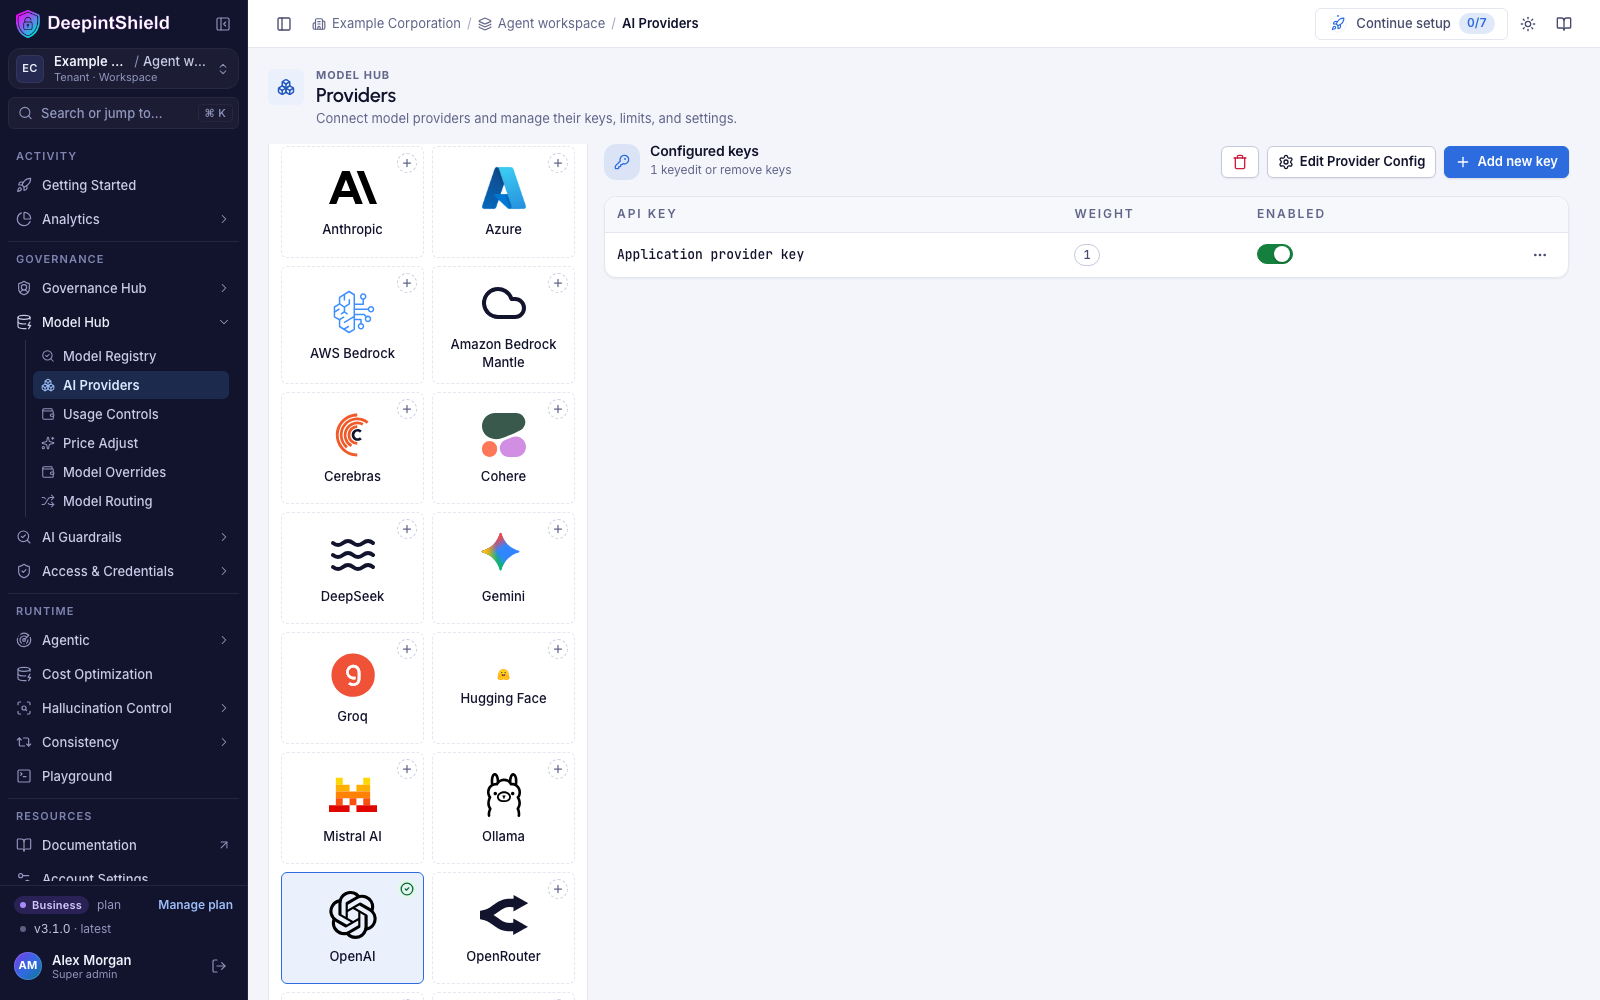
On DeepIntShield Cloud, everything is configured through the Web UI - there is no local file to edit. The hosted control plane persists all configuration for you and applies changes in real time.
Web UI Configuration
Section titled “Web UI Configuration”Sign in at https://app.deepintshield.com and configure everything visually:
- UI is enabled by default - configure everything in real time through the web interface
- Persistent storage - all changes save to the hosted control plane immediately, with no restart required
- Live monitoring - request logs, metrics, and analytics are available right in the dashboard
All provider, virtual-key, and MCP configuration is managed here - add providers and keys, create virtual keys, and connect MCP clients directly from the dashboard.
The Three Stores Behind Your Workspace:
- Config Store: holds provider configs, API keys, and MCP settings - powers the UI
- Logs Store: holds the request logs shown in the UI - optional, can be disabled
- Vector Store: backs semantic caching - optional, can be disabled
On DeepIntShield Cloud these stores are fully managed for you. If you self-host (Enterprise), you provision them yourself - see the Deployment Guides.
Next Steps
Section titled “Next Steps”Now that you have DeepIntShield running, explore these focused guides:
Essential Topics
Section titled “Essential Topics”- Provider Configuration - Multiple providers, automatic failovers & load balancing
- Integrations - Drop-in replacements for OpenAI, Anthropic, and GenAI SDKs
- Multimodal Support - Support for text, images, audio, and streaming, all behind a common interface.
Advanced Topics
Section titled “Advanced Topics”- Tracing - Logging requests for monitoring and debugging
- MCP Tools - Enable AI models to use external tools (filesystem, web search, databases)
- Governance - Usage tracking, rate limiting, and cost control
- Deployment - Cloud, Enterprise VPC, and self-hosted options
Happy building with DeepIntShield! 🚀